Our core product

SecCheck: Security and Compliance Analysis for Windows

Security and compliance analysis for Windows clients and servers: one read-only scan, one report with target values per standard and a risk score, one dashboard for the whole fleet. Evidence instead of estimates - for management, auditors and regulators, including NIS2 and DORA.

Overview

SecCheck is software by BitStream GmbH, Passau, for security and compliance analysis of Windows clients and servers: its analysis component SecCheck Report checks the configuration state read-only and without an agent against Microsoft Security Baselines, BSI IT-Grundschutz and SiSyPHuS, CIS Benchmarks and DoD STIGs. The software collects technical states automatically and creates a reliable basis for technical and organisational decisions.

The result is reproducible reports with which you can prove the security state of your systems to management, auditors and regulators - a documented evidence position instead of a mere estimate. SecCheck thereby supports evidence obligations under NIS2 and DORA, among others.

SecCheck is available as a single license, multi-pack or subscription; the collection runs entirely within your own environment, no permanent cloud or internet connection is required. Evaluation takes place in the SecCheck portal - or, with the Platinum license, entirely on your premises.
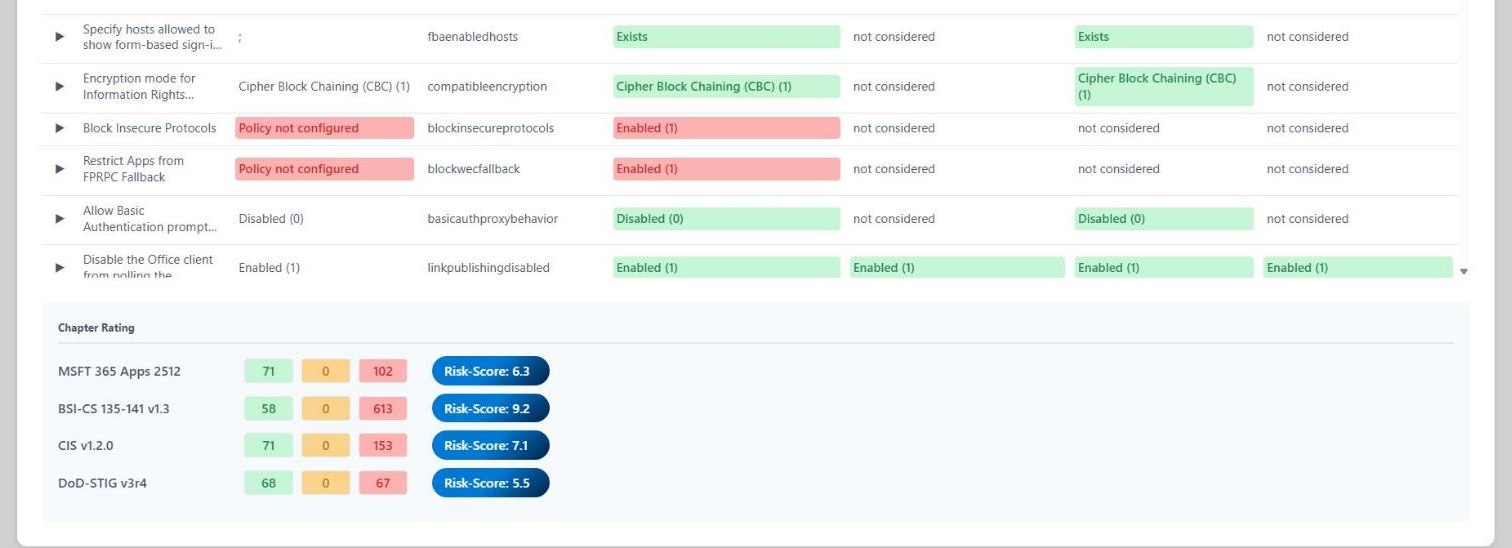
SecCheck report, chapter Microsoft Office 365: policies with actual and target values and the chapter rating with a risk score per standard

From the report: policies with actual and target values, below them the chapter rating with a risk score per standard (report shown in German).
How an analysis runs

  1. Provide the collector. SecCheck Report™ is portable: no installation, no agent, no service. The collector is downloaded from the portal and sits on a drive, a share or in your software distribution.
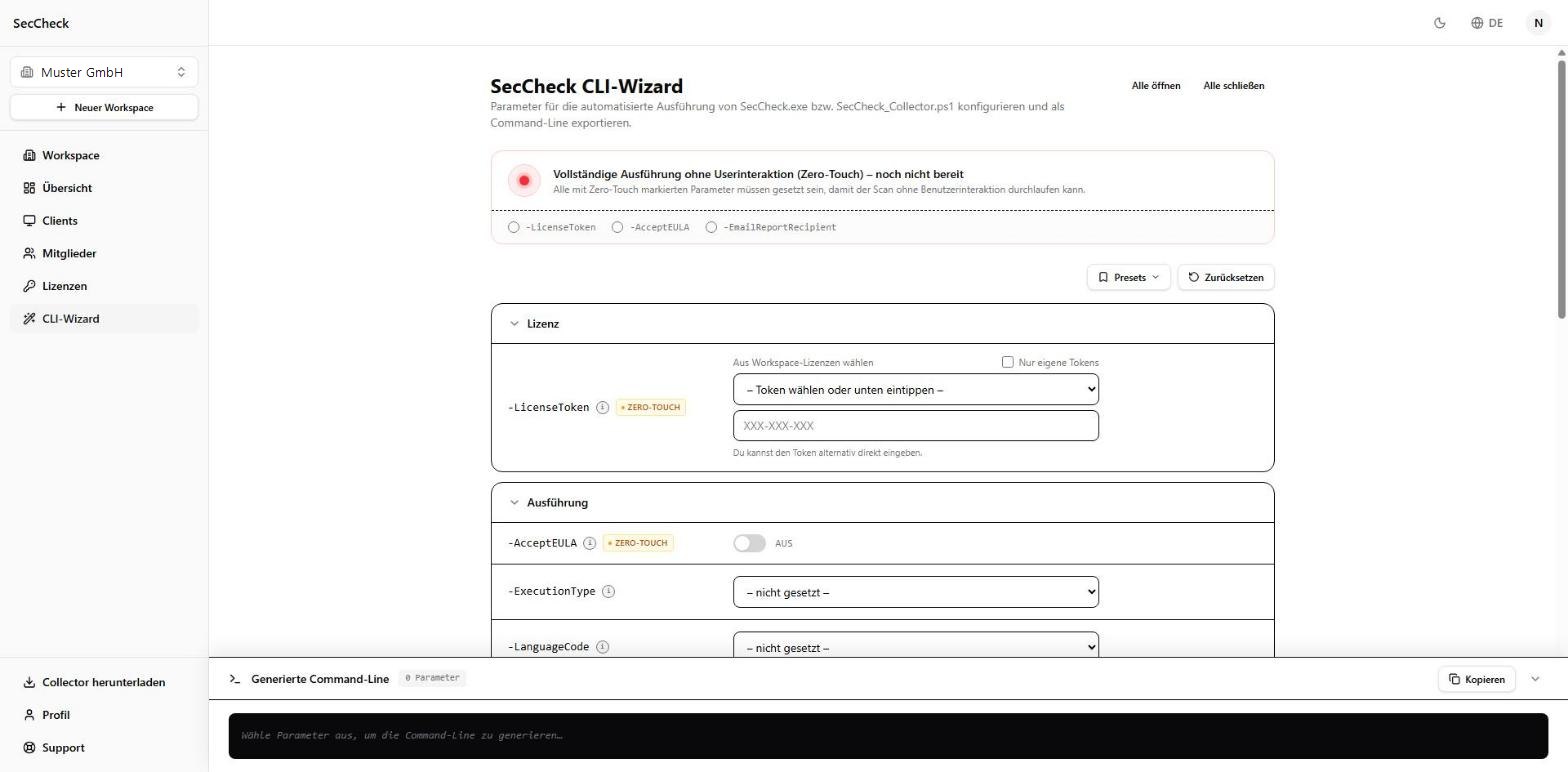
  2. Run the scan. Manually or automated through Intune, MECM, Group Policy or Task Scheduler. The CLI wizard in the portal builds the command line: license token, execution in computer or user context, scan mode Quick, Normal or Deep, report language, e-mail recipient, local storage path - and shows when a scan runs entirely without user interaction (zero-touch).
  3. Hand over the result. Collection is strictly read-only and produces machine-readable JSON. It is transmitted directly or - without internet - stored locally and handed over later in a controlled way.
  4. Report and dashboard. The portal turns every result into an HTML report, keeps the history per device and brings all devices of an organisation together in one dashboard.
SecCheck CLI wizard in the portal: parameters for license token, AcceptEULA, ExecutionType, LanguageCode and the zero-touch check, the generated command line at the bottom

CLI wizard: choose parameters, copy the command line, store it in your software distribution.

The report

Every scan yields a report per device - hardware, operating system, license, installed apps and then, chapter by chapter, the hardening: Windows, Microsoft Edge, Internet Explorer, Microsoft Office 365, Mozilla Firefox, OneDrive. For every policy, the device's value sits next to the target values of the standards - Microsoft Security Baselines, BSI SiSyPHuS, CIS Benchmarks, DoD STIGs and, on request, your own requirements. Green compliant, red deviating, "not considered" where a standard makes no statement.
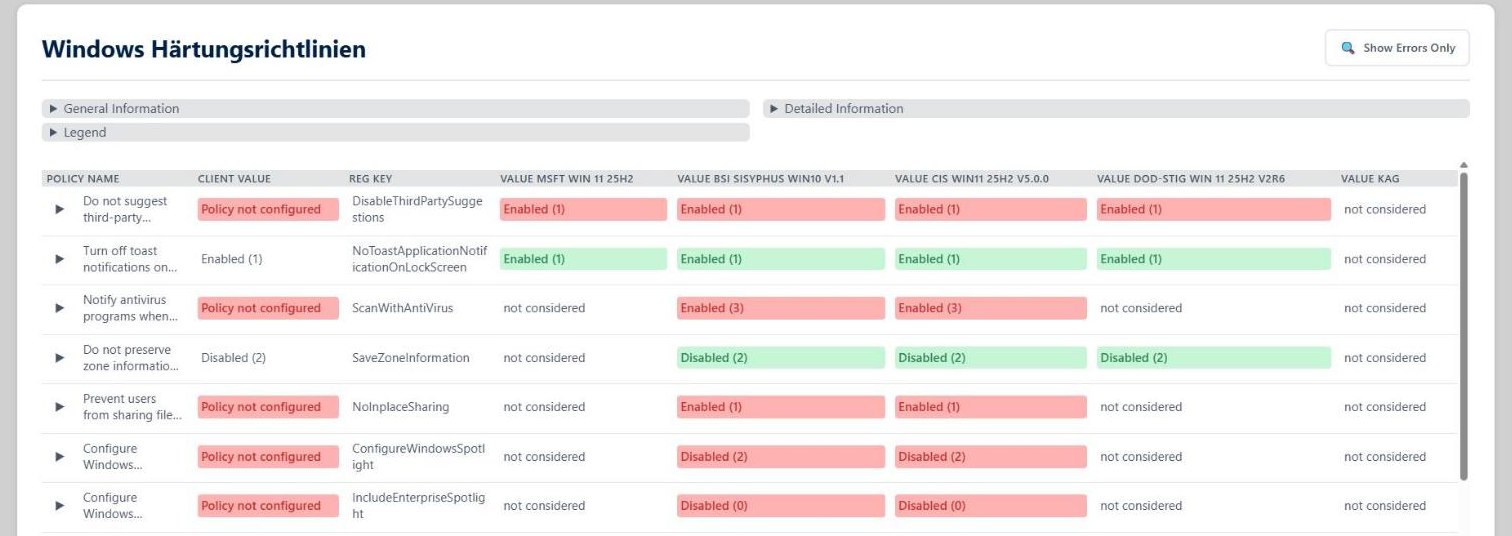
Report chapter Windows hardening policies: per policy the client value, the registry key and the target values according to Microsoft Win 11, BSI SiSyPHuS, CIS and DoD STIG, rated green or red
Chapter "Windows hardening policies": the device's actual value against the target values of four standards.

Every policy can be expanded. Underneath sit the GPO path and description, registry hive, path and type, the origin of the value, the ADMX source, severity, topic board and implementation effort. The administrator sees at once where to check the value and where to set it - no need to look it up in baseline documents.
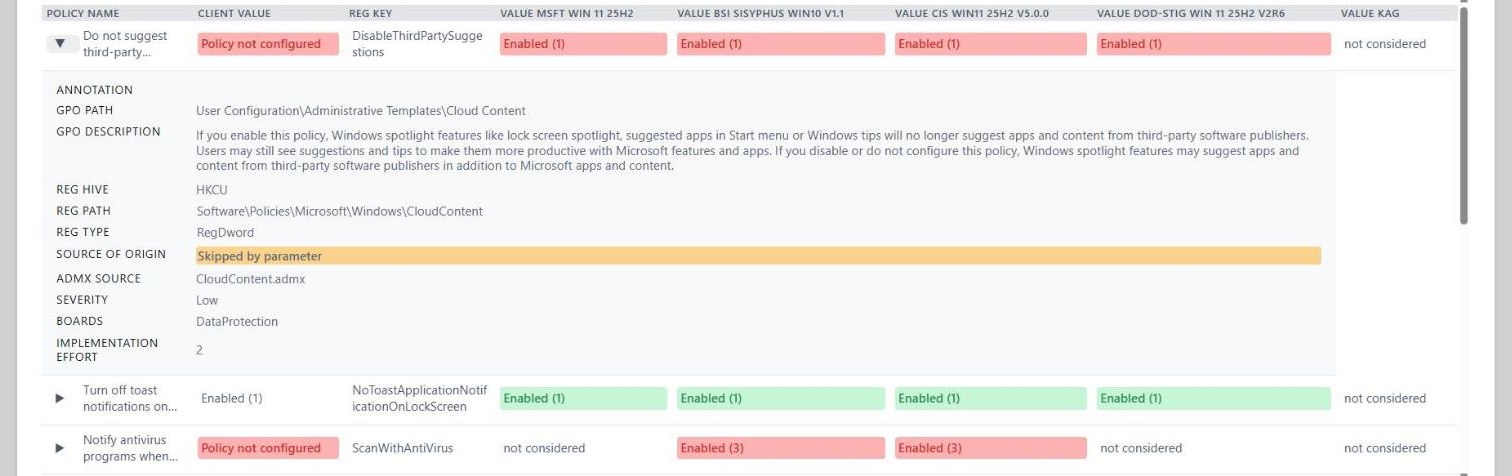
Expanded policy in the report: GPO path, GPO description, registry hive HKCU, registry path Software\Policies\Microsoft\Windows\CloudContent, type RegDword, ADMX source CloudContent.admx, severity, board and implementation effort
Detail view of a policy: registry key, GPO path and target values at a glance - check and set without detours.
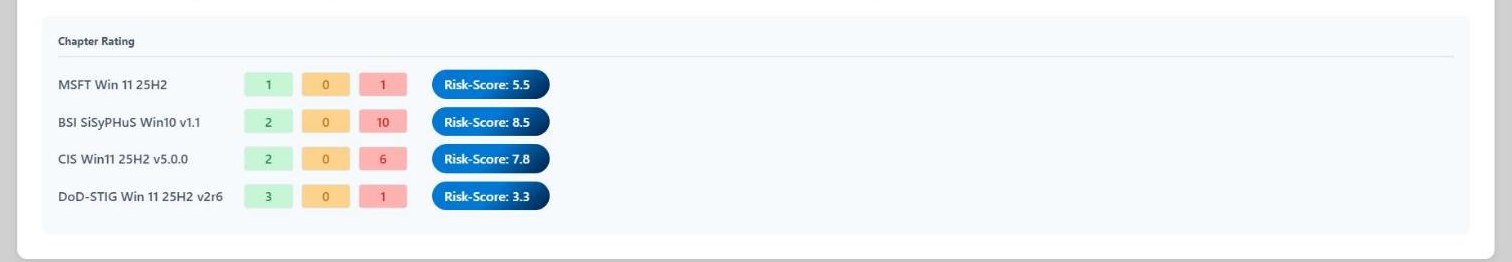
Chapter rating for Windows 11: number of compliant and deviating checks and risk score per standard - Microsoft, BSI SiSyPHuS, CIS, DoD STIG
Chapter rating: compliant and deviating checks per standard, condensed into a risk score.
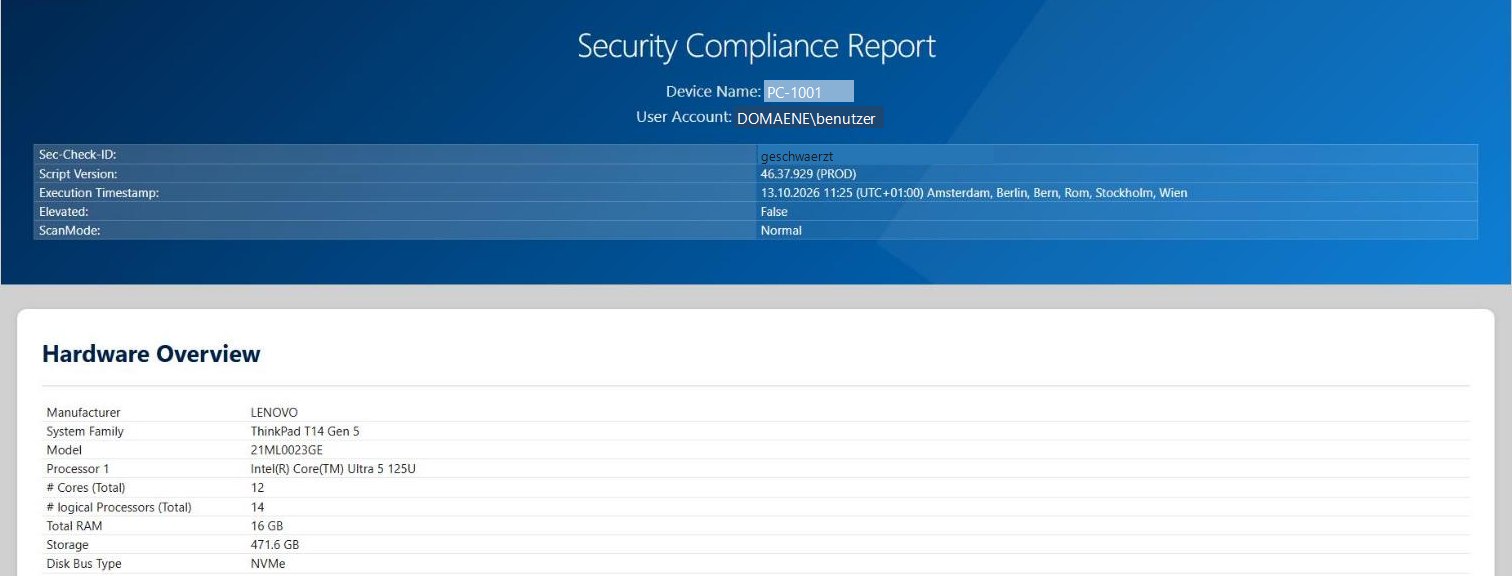
Header of a Security Compliance Report with Sec-Check ID, script version, timestamp, scan mode and hardware overview
Report header with collection metadata and hardware overview; device, user and ID redacted here.
  • Reproducible - the same check logic on every device, every run an independent snapshot with timestamp and script version.
  • Cross-framework - one check, several standards; deviations can be filtered per standard ("Show Errors Only").
  • Explained - general and detailed information and a legend for every chapter; the registry key for every policy.
  • In your own branding - partners deliver reports with their own logo and template.
  • In English or German - report language selectable per scan.

The portal

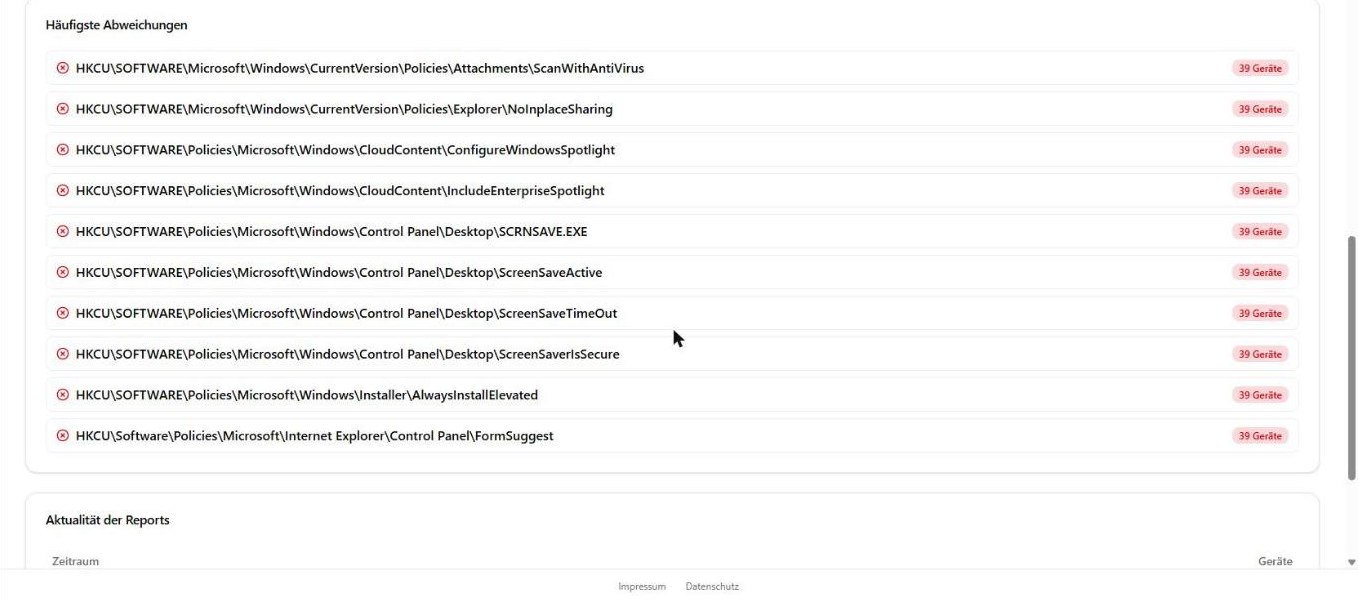
One workspace per organisation - IT service providers manage several customers separately. The dashboard shows where the fleet stands: devices, compliance rate, critical findings, endangered systems, findings by severity, compliance per chapter, the most frequently missed policies and the freshness of reports. The client list shows every device with manufacturer, model, domain, last report and report history.
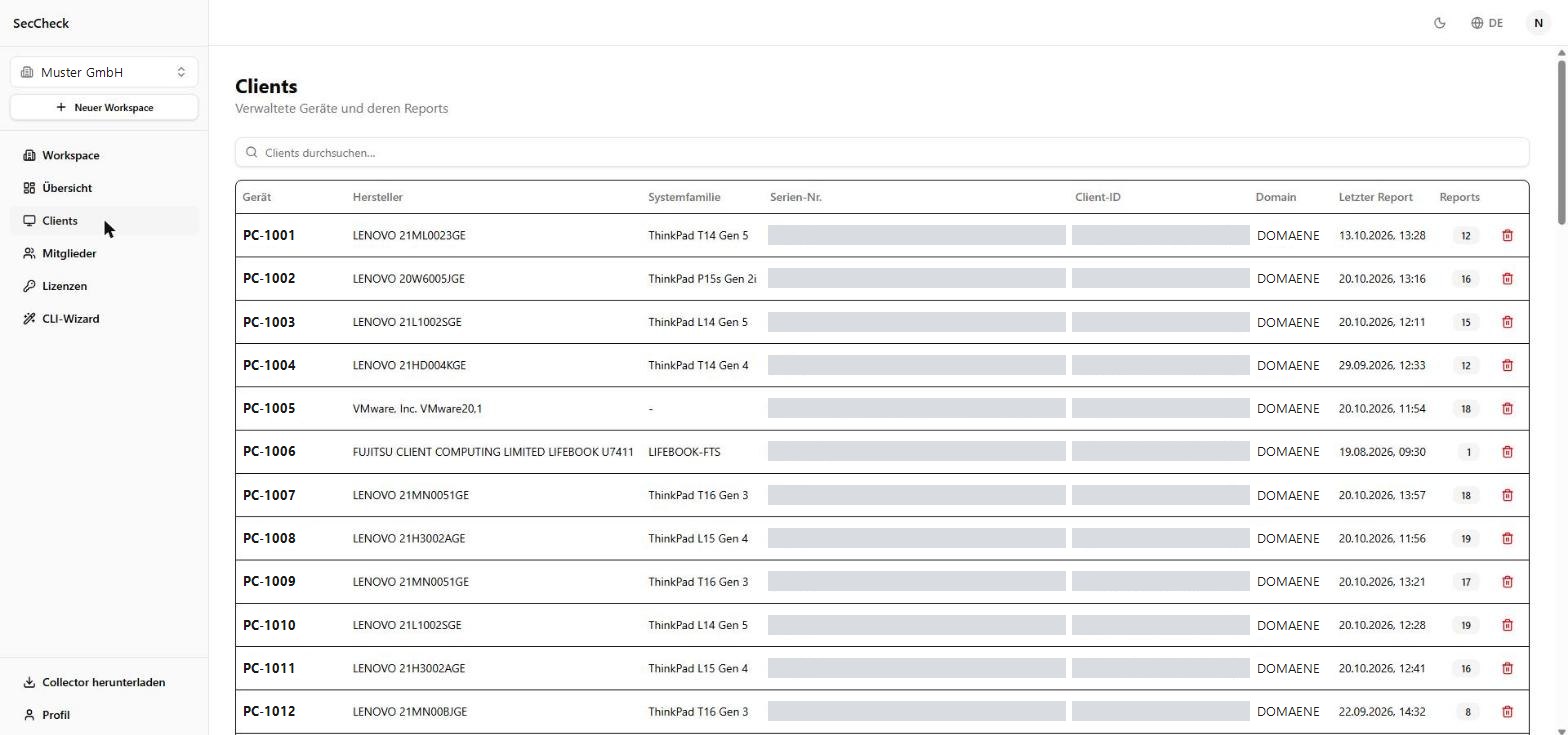
Client list in the SecCheck portal: device, manufacturer, system family, serial number, client ID, domain, last report and number of reports per device
Clients: managed devices and their reports (names, serial numbers and IDs redacted here).
Dashboard section most frequent deviations: registry policies with the number of affected devices
Most frequent deviations across all devices - shows which measure improves many devices at once.
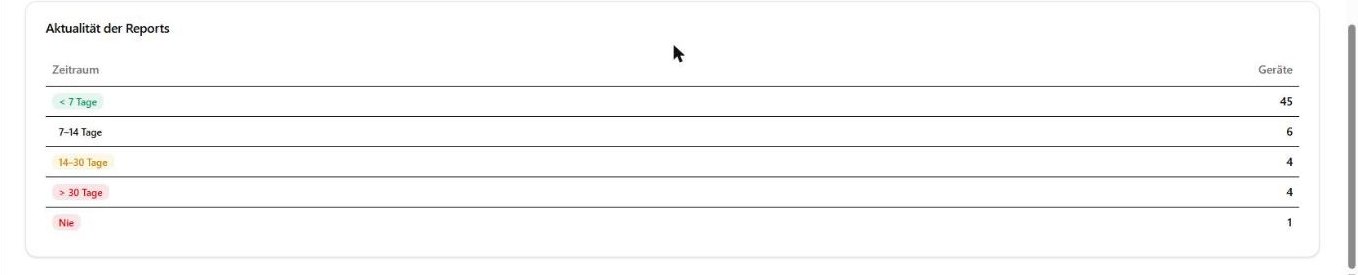
Dashboard section report freshness: devices by age of the last report
Report freshness: which devices have not been scanned for more than 30 days.
  • Members and roles per workspace, sign-in with Microsoft Entra ID.
  • Licenses and tokens per workspace; the token controls the collector.
  • History - reports are kept per device; drift analysis over time is in development.
  • English and German, light and dark.

What sets SecCheck apart

  • Read-only and forensically neutral
    SecCheck does not change the examined system: no system or program files, no registry values, no services; a result file is only written if you specify a local storage path. Results remain traceable and reliable.
  • Agentless and portable
    A one-off process that ends after collection - no installation, no permanent infrastructure.
  • Offline-capable
    No cloud or internet requirement; usable in isolated and regulated environments, results handed over later and in a controlled way.
  • Broad platform
    Windows 10 and 11, Windows Server from 2016 including Server Core; physical, virtual, Azure Virtual Desktop, Windows 365; domain-joined and standalone.
  • Extensible
    Your own checks and a company-specific compliance baseline for organisation-specific requirements.
  • Signed
    Collector and program carry an EV code signature.
  • Vendor-independent
    SecCheck maps verifiable system states without prescribing technical measures - the decision stays with you.

Product structure

SecCheck Report™

The read-only component for objective collection and evaluation of security-relevant system states - collector, report and portal. Available.

SecCheck Controls™

Optional implementation tools for specialised IT service providers and internal IT - never active automatically, always with deliberate approval. In planning, not part of SecCheck Report™.

Analysis and implementation are deliberately separated: SecCheck provides the technical basis for decisions; responsibility for assessment and implementation stays with the customer or the commissioned service provider.

SecCheck is not an EDR, SIEM or monitoring system, not a penetration test and not a vulnerability scanner, and it assesses Windows systems only; it does not replace an audit or certification but provides the technical evidence for it.

License and availability

SecCheck is used on a license basis - as a single license, multi-pack or subscription with a scan quota; every end-customer organisation receives its own license. Three tiers build on each other:

  • Silver - customer-specific checks and a company-specific compliance baseline.
  • Gold - additionally central evaluation and consolidation of several systems in the portal.
  • Platinum - operation entirely in your own environment, without external storage or processing; with an introduction project.

A trial license shows functionality and assessment logic with anonymised content; a proof of concept can be agreed per project. IT service providers and managed security service providers use SecCheck for several customers - with a partner area, customer management and a commission model.

Data sovereignty and neutrality

  • EU/EEA - processing exclusively within the EU/EEA jurisdiction, no transfer to third countries.
  • No disclosure - collected data does not go to third parties; every handover is deliberate and controlled.
  • Data-minimising - technical configuration and status data is collected; accounts and profiles can be pseudonymised, the software inventory switched off.
  • Independent - SecCheck is designed as a vendor-independent solution and maps system states without prescribing measures.

Who SecCheck is built for

SecCheck addresses organisations that have to prove their security and cannot interrupt operations to do so. The industry overview on seccheck.io (German) describes the requirements per industry; defence and the public sector are presented here on bitstream.de.

Public sector

Federal, state and local government, universities, municipal IT providers

Documented hardening per device for audits, internal review and procurement.
  • BSI IT-Grundschutz
  • NIS2
  • ISO 27001

Defence

Defence-related organisations and suppliers to the defence industry

Assessment and deployment without internet, evidence per device, controlled supply chain through a data lock.
  • Classified information
  • ISO 27001
  • DoD STIGs

Energy and utilities (seccheck.io, German, new tab)

Municipal utilities, energy suppliers, grid operators, water and wastewater

Documented configuration for certification audits and regulatory evidence, including segregated networks.
  • ISO 27001
  • IT-Sicherheitskatalog
  • KRITIS
  • NIS2

Healthcare (seccheck.io, German, new tab)

Hospitals, clinics, medical centres, practices, laboratories, rehabilitation and care

Security checks without interrupting patient care or operations.
  • KRITIS
  • B3S
  • NIS2
  • GDPR

Financial services (seccheck.io, German, new tab)

Banks, savings banks, insurers, asset managers, payment and leasing providers

Evidence of ICT risk management, preparation for super­visory and auditor reviews.

  • DORA
  • MaRisk
  • ISO 27001

Industry and suppliers (seccheck.io, German, new tab)

Automotive and machinery suppliers, chemicals, pharma, medical devices, logistics

Customers, auditors and regulators demand documented hardening rather than policies alone.
  • TISAX
  • GxP
  • NIS2
  • ISO 27001

Law, tax and audit firms (seccheck.io, German, new tab)

Lawyers, notaries, patent attorneys, tax advisors, auditors

Protecting client confiden­tiality, pragmatic assess­ment without an IT department of your own.
  • § 203 StGB
  • GDPR
  • Professional rules

The requirements named above, in one sentence each

The tiles name the requirements each industry is measured against. Here is what they stand for, in brief. SecCheck provides the technical evidence per device for them, but does not replace a legal assessment.

NIS2
EU directive on cybersecurity, implemented in Germany through the BSI Act: important and essential entities must manage risks, report incidents and prove their measures; the management body is responsible for this.
KRITIS
Operators of critical infrastructure (energy, water, health, IT, transport and others) under the German BSI Act and the KRITIS ordinance: implement the state of the art, prove it every two years, report disruptions.
BSI IT-Grundschutz
Methodology and catalogue of building blocks by the German BSI for an information security management system; the benchmark for federal authorities and the basis of the certification "ISO 27001 based on IT-Grundschutz".
ISO 27001
International standard for information security management systems, certifiable; requires, among other things, hardened, documented and monitored system configurations.
BSI C5
Criteria catalogue of the German BSI for cloud and data centre services; providers have compliance attested by auditors.
DORA
EU regulation on digital operational resilience in the financial sector, applicable since 17 January 2025: ICT risk management, testing, incident reporting and oversight of ICT service providers.
MaRisk
BaFin circular with minimum requirements for the risk management of banks; specifies the duties for organisation, risk control and IT under the German Banking Act.
IT-Sicherheitskatalog
Catalogue of the German Federal Network Agency under section 11 of the Energy Industry Act for electricity and gas grid operators and energy plants: a certified ISMS to ISO 27001 is mandatory.
B3S
Industry-specific security standards, for example the B3S for hospitals by the German Hospital Federation; recognised by the BSI as suitable to meet the KRITIS requirements.
TISAX
Assessment and exchange mechanism of the automotive industry (ENX, based on the VDA ISA) for the information security of suppliers; assessed by accredited providers, results are shared among manufacturers.
GxP
Collective term for the good practice rules in pharma and medical technology (GMP, GLP, GCP): IT systems must be validated, traceable and tamper-proof, for example under EU GMP Annex 11 and 21 CFR Part 11.
Classified information
Rules for handling classified material under the German Security Clearance Act and the classified information directive, in industry under the Geheimschutzhandbuch; requires approved, documented and controlled IT.
DoD STIGs
Security Technical Implementation Guides by DISA (US Department of Defense): detailed hardening requirements per product, used internationally as a reference for system hardening.
GDPR
EU General Data Protection Regulation; Article 32 requires technical and organisational measures in line with the state of the art, Article 5(2) the proof that they work.
KDG und DSG-EKD
Church data protection laws of the Catholic Church (KDG) and the Protestant Church (DSG-EKD), which take the place of the GDPR for church and social welfare organisations, with their own supervisory bodies.
§ 203 StGB and professional law
Criminal provision protecting private secrets held by doctors, lawyers, tax advisors and other professionals bound to secrecy; since 2017 paragraph 3 governs the involvement of IT service providers, and the professional codes add IT security requirements.
StaRUG
German Corporate Stabilisation and Restructuring Act, in force since 1 January 2021; section 1 obliges the managing directors of limited liability companies to continuously monitor developments that could threaten the company's existence and to counteract them.

Management and IT security

A severe IT security incident can be such a development. For the managing directors of a GmbH, AG, UG, gGmbH or cooperative this means: they must know and monitor the state of IT security with the diligence of a prudent businessperson (section 43(2) GmbHG, section 93(2) AktG). The German NIS2 implementation additionally requires the management body to approve the risk management measures, to oversee their implementation and to attend training. Public authorities do not fall under the StaRUG, municipal companies in private legal form do. SecCheck provides the documented state per device for this: traceable, repeatable, as a report. It does not replace a legal assessment.

Get to know SecCheck

All details on scope, industries and the partner model are on the SecCheck product website, plus an anonymised sample report and frequently asked questions on licensing and operation (both in German) - or talk to us directly.

Or directly: +49 851 204248-0 · info@bitstream.de