Industry: Public sector
IT security for public authorities and public institutions
Verifiable, data-minimising, from Germany: tools that prove the security state of your Windows systems, work without mandatory cloud and take work off your helpdesk. For federal, state and municipal administrations, universities, schools, municipal data centres and public-sector IT service providers.
What public authorities get from us
Evidence instead of estimates
Audit offices, the BSI and supervisory bodies ask for evidence, not impressions. SecCheck reads Windows clients and servers without changing them and assesses them against BSI IT-Grundschutz and SiSyPHuS, CIS Benchmarks and Microsoft Security Baselines - reproducibly, with timestamp and script version. The report supports the NIS2 implementation and the preparation for audits.
Tools without cloud dependency
Collection runs without internet; evaluation takes place in the EU-hosted portal or, with the Platinum license, entirely in your own data centre. Win-INNsider and File-INNsider work locally, without telemetry and without an account. Data minimisation is a design goal for us, not a setting.
Short paths to the vendor
No hotline queue, no chatbot without a contact person: with us you reach people, namely the ones who build the tools. Questions from procurement, data protection and audit we answer directly - with the document you need for it.
Few staff, many sites
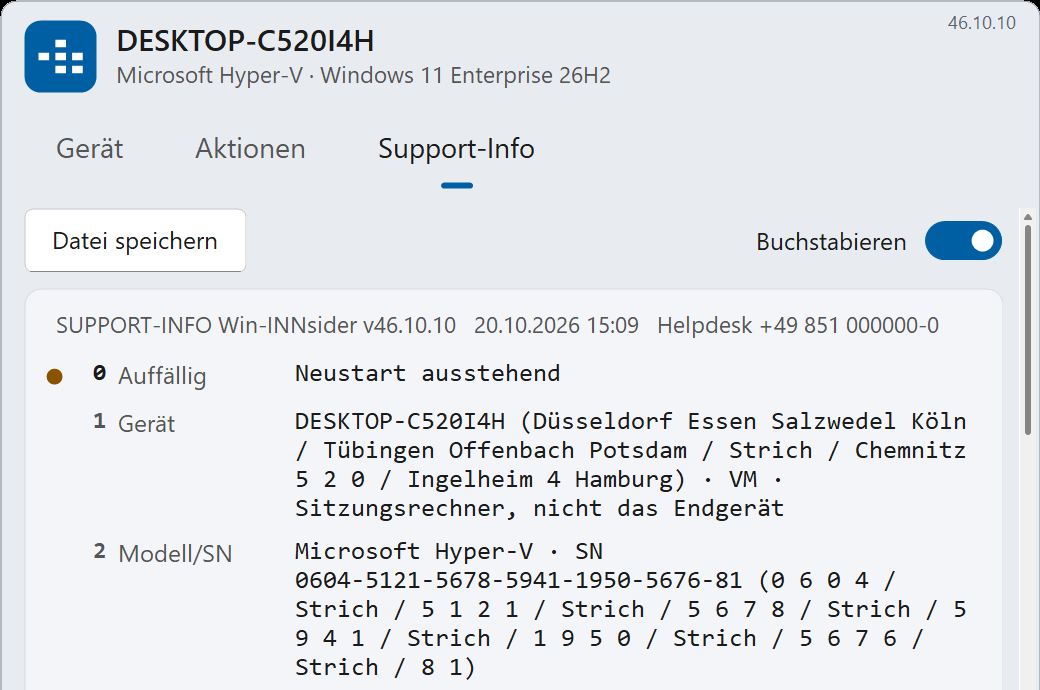
Administrations often support many sites with small teams and support by phone. Our free tools shorten exactly these paths: the support info in fixed lines for the helpdesk, the origin of an installation package at a glance - distributed by Group Policy, without additional runtimes, light and dark like Windows.
Our products for public authorities
SecCheck - the evidence for auditors
Read-only scan without an agent on Windows 10 and 11 and Windows Server from 2016; report per device with target values according to BSI, CIS, Microsoft and DoD STIGs, risk score per chapter; dashboard per organisation with the most frequent deviations and the freshness of reports. Rollout through Group Policy or Task Scheduler, no installation. For IT-Grundschutz evidence, NIS2 implementation and audit preparation.
SecCheck product page · Public sector page on seccheck.io (German) (new tab)
Win-INNsider - the helper for the helpdesk
Shows the user device name, serial number, network and Windows build in a flyout and delivers the support info in fixed lines - the computer name spelled out on request according to DIN 5009 so nothing goes wrong on the phone. Quick toggles for touch display, presentation mode and power; rollout as MSI through Group Policy, Intune or MECM. Free; public authorities register, a support contract is optional.
More about Win-INNsiderFile-INNsider - proving the origin of packages
Before an installation package is approved: Authenticode signature with signer, issuer and status, checksums from MD5 to SHA-512 - in the Explorer context menu, offline, with an explanation for every error code. "Copy all" delivers the text block for the approval record. Free, as a signed MSI.
More about File-INNsideromniDEPLOY - deployment for special cases
Citizen and training terminals, kiosk systems, special workstations and isolated networks that never see Intune or Active Directory: installation by network boot with Secure Boot enabled, hardening to BSI, CIS or Microsoft included, evidence per device. On-premises or as SaaS, introduction as a project.
More about omniDEPLOY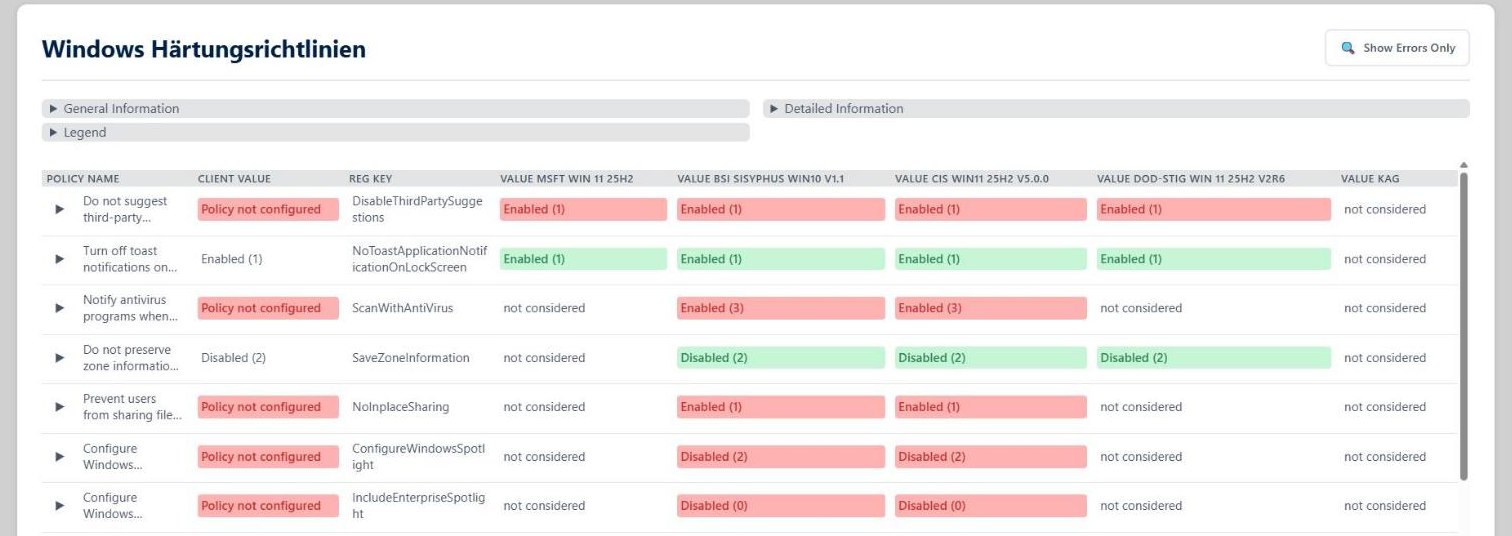
Standards and requirements
- BSI IT-Grundschutz
- Assessment of Windows hardening against BSI requirements (IT-Grundschutz, SiSyPHuS) in SecCheck; hardening layers to BSI in omniDEPLOY; server operation to IT-Grundschutz building blocks
- NIS2
- Reproducible evidence of the security state per system with timestamp and script version; dashboard for the state of the whole fleet
- ISO 27001
- Technical evidence for ISMS audits, often based on IT-Grundschutz; report per device with timestamp and script version
- CIS Benchmarks
- Target values per policy in the SecCheck report; hardening to CIS Level 2 in omniDEPLOY
- Microsoft Security Baselines
- Target values per policy in the SecCheck report; as a hardening layer in omniDEPLOY
- DoD STIGs
- Additional mapping per policy in the SecCheck report where the audit requirement demands it
- GDPR
- Processing exclusively within the EU/EEA; technical configuration data instead of personal data, accounts and profiles can be pseudonymised, software inventory can be switched off; no telemetry in the tools
- Accessibility
- Accessibility statement for this website under the German BFSG, oriented to WCAG 2.1 AA; the tools follow the light and dark Windows scheme
For procurement
What procurement offices need to know about the supplier is here - without a detour through a sales call:
- German vendor - BitStream GmbH, based in Passau, founded in 2014; participant in the BSI's Alliance for Cyber Security; research project certified by the BSFZ (German research allowance).
- Self-financed - entirely from our own resources, independent of external investors.
- License models, no surprises - SecCheck in the tiers Silver, Gold and Platinum as single license, multi-pack or subscription; Win-INNsider and File-INNsider free of charge, public authorities register - free with consent to the use of the e-mail address, paid with a support contract.
- Signed software - programs and installation packages carry an EV code signature; checksums are published on the product pages.
- Documents on request - data protection description, processing overview, license terms and technical descriptions for your procurement documents.
Consulting from practice
More than 20 years of projects with federal authorities, critical infrastructure operators and large enterprises have gone into our tools - and into our consulting: baseline assessment with SecCheck, action plan by risk and effort, hardening to BSI, CIS and Microsoft, Active Directory tiering, support right up to the evidence for the audit. Measuring instead of estimating - in consulting too.
Talk to us
Whether IT-Grundschutz evidence, NIS2 implementation, helpdesk relief or terminals without a domain: tell us your starting point and we will answer with the tool that fits - and say so if none does.
Or directly: +49 851 204248-0 · info@bitstream.de